
Silo Admin Console Policy: 2-Factor Auth
Important: Please make sure to set a valid phone number for all applicable Silo accounts prior to enforcing this policy.
Steps
1. Launch the Silo Admin Console and click Manage under Policies

2. Navigate to the appropriate org --or-- sub-org you wish to implement the policy in

3. Expand Access & Authentication and click Edit

4. Select one of the following 2FA options:
- Never
- Untrusted
- Always
- Optional: Allow user override

5. Click Save to apply the change, close out and start a new Silo session for the policy implementation
User-Level 2FA Setting
If the admin has enabled Allow user override on the 2FA policy, individual users can set their own 2FA preference, independent of the org default:
1. In Silo, open User Settings (top-right menu)
2. Click 2-Factor Authentication
3. Choose one of:
- Never require it
- Require it only when I’m using an unrecognized device
- Require it every time I access Silo
4. Click Edit to change, then save
Note: This control only appears/works if the admin has checked "Allow user override" in the Admin Console policy. If that box is unchecked, users cannot change this setting — it always follows the org-wide policy the admin configured.
Common Issues
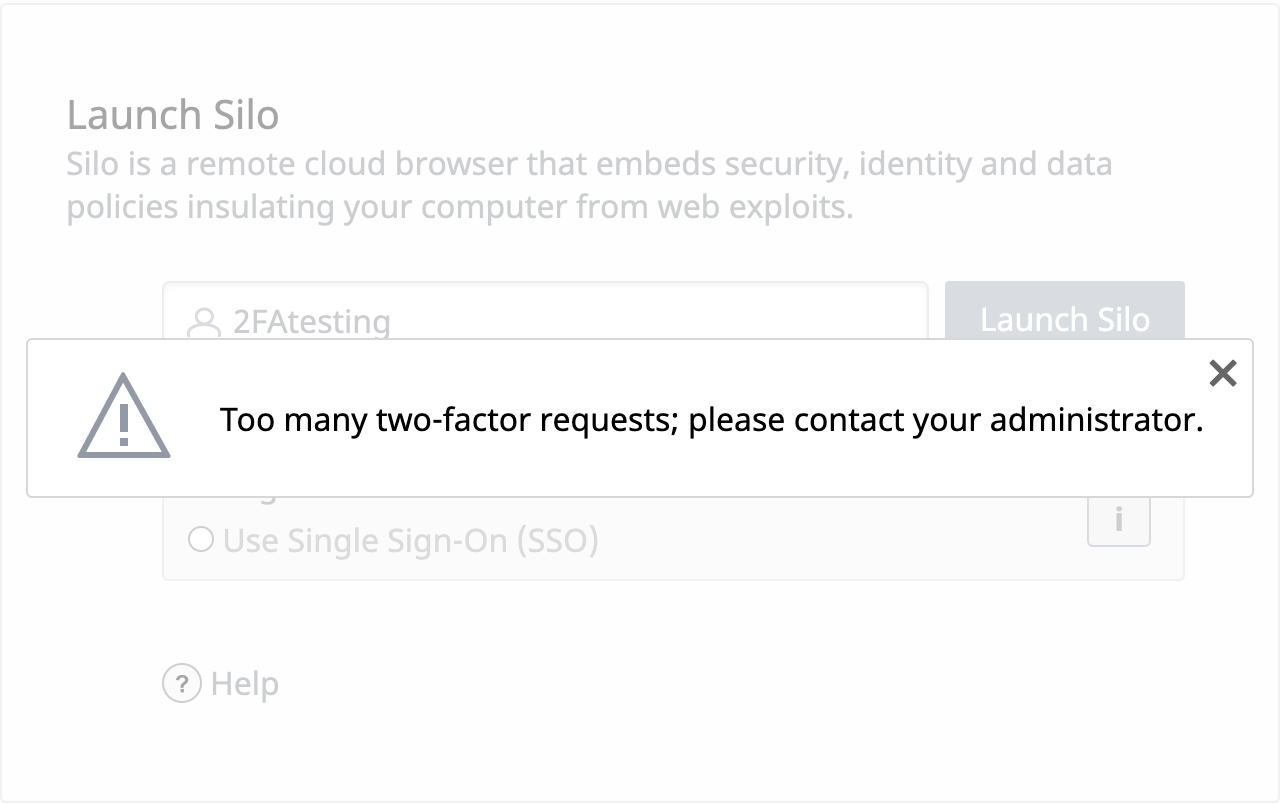
Important: Ensure that the verification code is input correctly, after several failed attempts a waiting period will be implemented. An additional failed attempt after the waiting period, users will be redirected to contact their Silo Administrator.
Please contact Support for any additional questions